
All Articles
Filter by Category
Archive
- Tradecraft & Analyst Skills
- Productivity & Reporting
- Generative AI
- Writing & Communication
- Cyber Threats & Security
- Humans & AI
- Search & Discovery
- Help Center
- emergency response
- geopolitical
- OSINT
- Live Events
- Popular
- Templates
- Wild Dog AI Podcast
- Corporate
- Finance
- Medical
- Communication Strategy
- Politics
- Private Investigation
Critical Thinking Is the Best Governor of AI
The Army promised its workforce unlimited AI access in May 2026. By mid-June, they'd burned through an entire year's token allocation. Meta and Uber hit the same wall. The problem was never the token limit — it's that critical thinking, not usage caps, is what actually governs whether AI creates value or just noise.
Intelligence Reporting for NGOs Operating in High-Risk Environments
A three-person NGO security team is expected to produce the same structured, multi-stakeholder reporting as a fully-staffed government operation — same checkpoints, same stakes, a fraction of the people. Here's what a lean, analyst-controlled reporting workflow actually looks like for teams that can't afford a full GSOC.
Deepfakes Are Now a Threat Intelligence Problem, Not Just a Communications One
A fabricated audio clip of your CEO starts circulating at 9:47 a.m. By 10:15, your stock is down and a reporter is asking if it's real — before your own team even knew it existed. Here's why deepfakes have moved from a communications risk to a threat intelligence problem, and what a response workflow needs to look like before that call comes in.
Campus Security Teams Are Building Intelligence Functions. What Does That Actually Require?
Campus security teams are now expected to run behavioral threat assessments, monitor online grievance narratives, and plan for predictable flashpoints — all with a fraction of the staff a dedicated intelligence unit would have. Here's what closing that gap actually requires, and where AI helps versus where it doesn't.
Designing a Repeatable Briefing Process for Intelligence
Analysts aren't losing time to bad instincts — they're losing it to rebuilding the same source collections, templates, and reviews from scratch every cycle. Here's why consistency in intelligence output is an infrastructure problem, not a discipline one, and what changes when the scaffolding actually holds.
A Generation of Analysts Is Learning to Use AI Before They Learn to Think Like Analysts
AI fluency and analytical judgment aren't the same skill — and right now, one is being trained at the expense of the other. Here's what's actually being lost as teams race to adopt AI, and what it takes to build analysts who think with AI instead of just using it.
What Private Equity Due Diligence Looks Like When AI Is in the Workflow
Private equity deal timelines demand both speed and defensibility — and most AI tools only deliver one. This post examines what enhanced due diligence research actually requires when findings need to travel from analyst to investment committee to LP scrutiny, and how a structured AI workflow built around curated source collections and embedded citations changes what analysts can produce and stand behind.
The After-Action Report Nobody Reads, & How to Fix It
Most after-action reports end up in a shared drive folder that nobody opens twice. They arrive too late, cover too much ground, and leave the reader doing the analytical work the report was supposed to do for them. This post follows Ted — an analyst who cracks the AAR problem not through better writing, but through a smarter workflow — and breaks down exactly how he produces structured, readable, actionable after-action reports in under an hour.
Election Cycles Are the Hardest Intelligence Environment to Report In. Here's Why.
Election cycles don't just create more work for intelligence analysts — they fundamentally alter the conditions under which reliable analysis is possible. Disinformation moves faster than verification, source credibility degrades under political pressure, and the demand for defensible assessments peaks precisely when the information environment is least trustworthy. This post examines what structured, defensible election-cycle intelligence actually requires and how to build the reporting infrastructure before the cycle puts it to the test.
What the First LLM-Driven Intrusion Means for SOC Reporting Workflows
On May 10, 2026, Sysdig documented the first known intrusion in which an LLM agent drove every decision in the post-exploitation phase — from initial access to a fully exfiltrated internal database — in under sixty minutes. This post breaks down what actually happened, why it represents a genuine category shift in the threat landscape, and what it means for the SOC reporting workflows that were built for a slower kind of adversary.
How Pharmaceutical Companies Are Using Intelligence Reporting to Track Supply Chain Risk
Most pharmaceutical supply chain teams find out about sourcing problems the same way everyone else does — through a news alert or a supplier email that arrives after the disruption has already started. This post breaks down what proactive pharma supply chain intelligence actually looks like: how to monitor API sourcing risk in sanctioned regions, what DSCSA enforcement means operationally in 2025–2026, how tariff volatility is reshaping network design decisions, and where AI-powered predictive alerting adds genuine value.
How Travel Risk Assessments Are Evolving
A travel risk assessment produced on Monday can be outdated by Thursday. In threat environments that shift within hours — civil unrest, weather disruptions, rapidly changing health advisories — static country reports can't keep pace. This post breaks down why the traditional model is no longer sufficient, what a modern travel risk assessment actually requires, and how GSOCs are adapting their workflows to meet a duty of care standard that has grown significantly more demanding.
The 4:45 PM Tasker: How Analysts Use GenAI When Leadership Needs Answers Before COB
At 4:47 PM, Mira gets a Slack message: leadership needs a geopolitical intelligence brief on the South Caucasus, presentation-ready, by close of business. This post walks through exactly how she builds it — from scoping the intelligence question to curating a source collection, generating a structured first draft, and delivering a fully cited, defensible product in under two hours.
What Happens When Your Intelligence Tool Goes Down During an Active Incident
At 2:31 AM, the intelligence platform goes offline. The analyst still has raw telemetry and endpoint logs — but the analytical layer tying it all together is gone. This post walks through what platform failure actually costs during an active incident, what mission-critical continuity requires from any AI intelligence tool, and the six questions every procurement team should be asking before they sign a contract.
AI SITREPs for SOC Teams, Fusion Centers, and Security Operations
A SITREP is only useful if it arrives before the window for action closes — and producing one manually under time pressure has always been the hardest part. This post breaks down how AI-assisted reporting changes the production workflow for three distinct security environments: SOC teams managing active incidents, fusion centers reconciling multi-agency source streams, and enterprise security operations maintaining consistency at scale.
When AI Becomes the Source: Why Analysts Matter More Than Ever
The CNN vs. Perplexity lawsuit is about copyright on the surface. Underneath, it points to something more consequential: a growing number of professionals are consuming information through AI summaries rather than original sources. This post examines what gets lost in that compression — nuance, caveats, uncertainty, competing perspectives — and why analyst judgment has never been more important than it is right now.
The Watchfloor Approach to Brand Intelligence
Most organizations treat reputation management as a communications function: monitor casually, react when something breaks, issue a statement, move on. But in a threat environment where a coordinated disinformation campaign can generate press coverage before the morning standup is over, that posture isn't enough. This post applies the operational logic of an intelligence watchfloor — continuous monitoring, structured assessment, rapid escalation — to brand risk, and walks through a four-stage intelligence cycle that turns reputation management from a reactive cleanup exercise into a proactive discipline.
Why Section-Level Regeneration Produces Better AI Reports
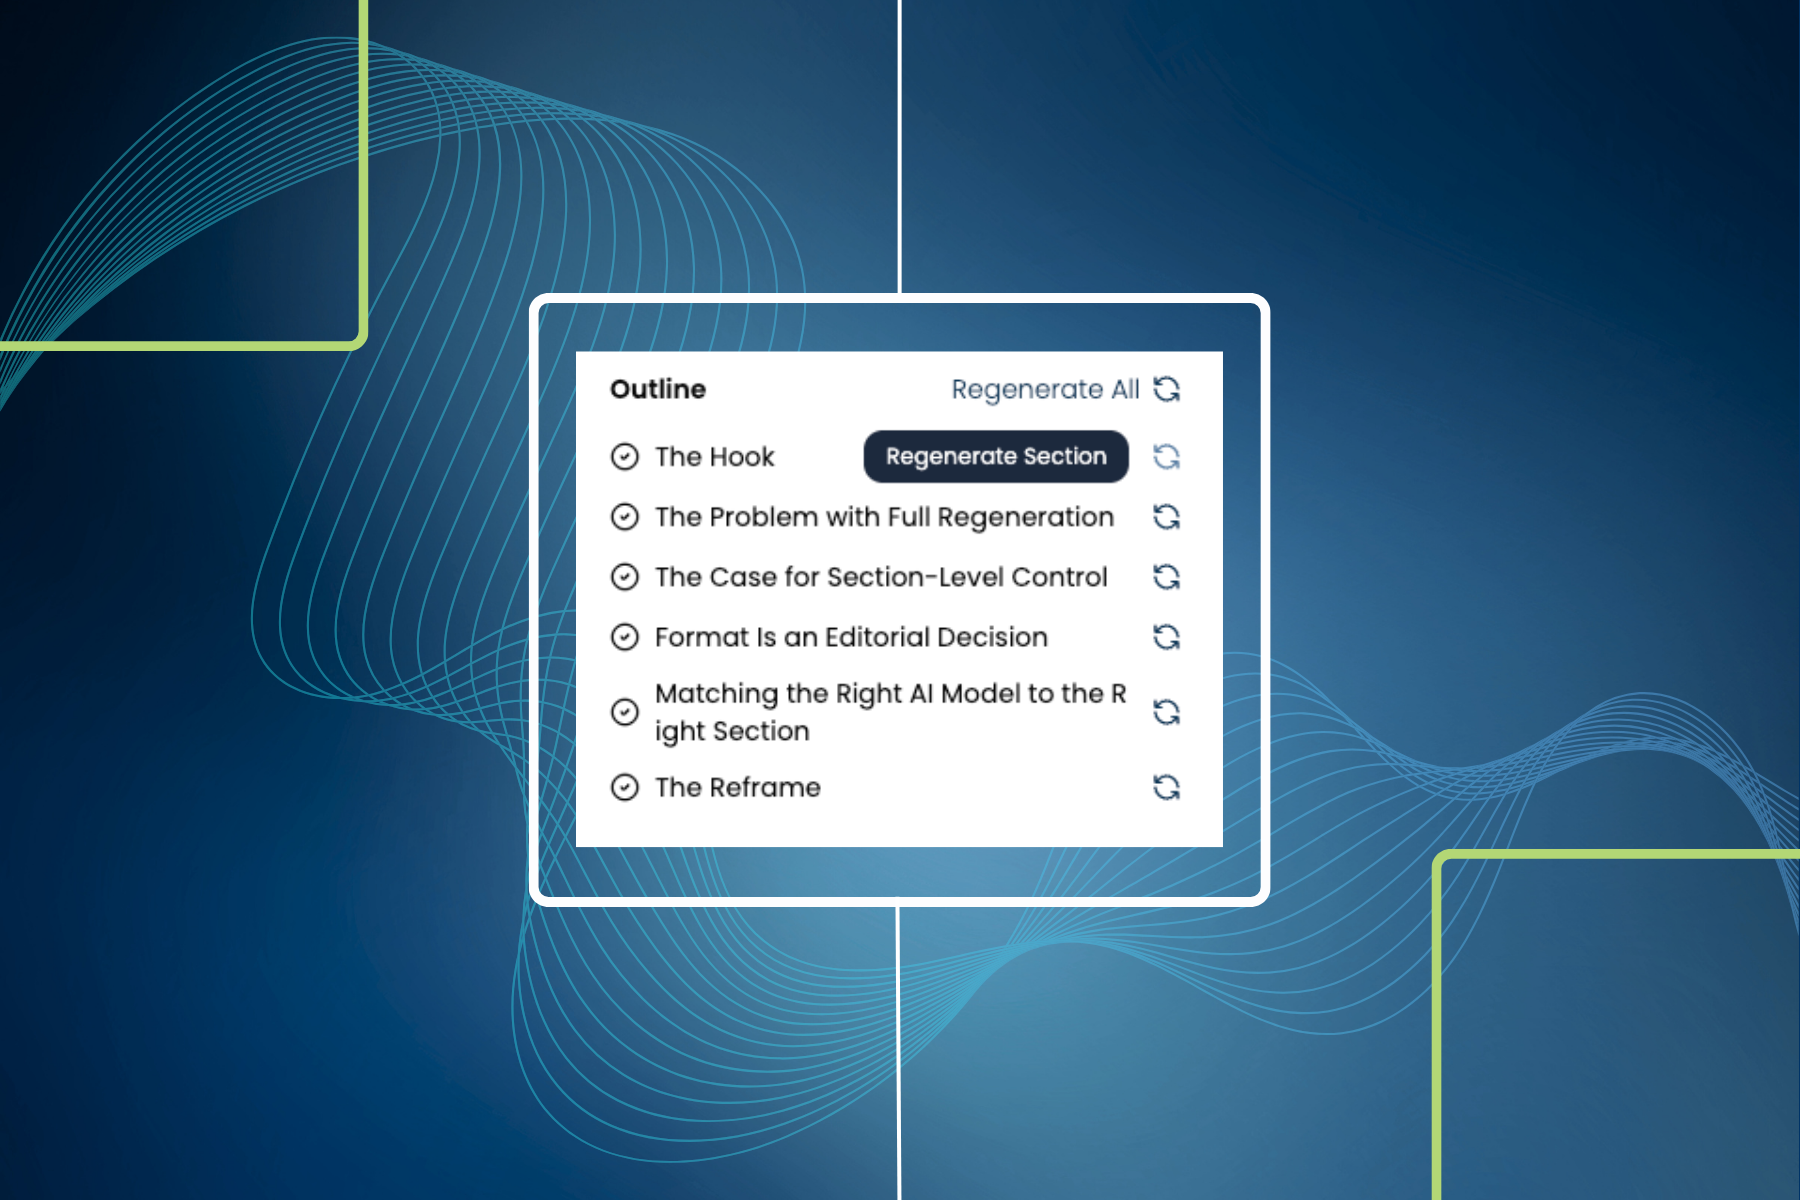
Most analysts have been there: one weak section in an otherwise solid report, and the temptation to hit regenerate and start fresh. The problem is that full regeneration treats every section as equally flawed — wiping out verified work to fix one paragraph. This post breaks down why section-level control produces better reports, how targeted instructions outperform global rewrites, and how matching the right AI model to the right section changes the quality of the final product.
Brand Intelligence Isn't Just for Marketing Anymore
Brand risk isn't a marketing problem anymore. A deepfake, a data breach, or a coordinated disinformation campaign can trigger consequences across security, legal, investor relations, and HR simultaneously. Here's why cross-functional brand intelligence is now a mission-critical input — and what it looks like when it works.
What Happens When You Run Intelligence Reporting Through ChatGPT Instead of a Controlled Platform
General-purpose LLMs like ChatGPT are fast, accessible, and genuinely useful for early-stage research. They are also structurally unreliable for professional intelligence reporting — generating confident-sounding text that may have no grounding in a verifiable source, with no citation trail, no audit record, and no way to reproduce the output six months later when someone asks where it came from. This piece examines three dimensions where the two approaches diverge most sharply: hallucination risk, source attribution, and audit trail — and offers a clear framework for deciding which tool belongs where in a professional intelligence workflow.